Quick answer
Choose a multi tenant live streaming platform when several brands, agencies, creator groups, schools, or consultation businesses must operate independently on shared streaming infrastructure. Separate each tenant’s domains, branding, users, permissions, rooms, payment configuration, reporting, moderation work, and exports. Share video and operational services only behind enforced tenant identifiers, quotas, audit logs, and tested failure boundaries.
When a multi tenant live streaming platform is the right model
Use multitenancy when one operator must support independently branded streaming businesses without maintaining a separate product stack for every brand. The tenant should represent the commercial entity that controls configuration, staff, creators, audiences, reporting, and revenue rules—not an individual viewer account.
The expensive mistake is treating a creator, agency, school, or consultation brand as an ordinary user with extra permissions. That shortcut works until the first agency requests its own domain, staff roles, payout policy, moderation queue, and export. Retrofitting a tenant boundary then touches authentication, database queries, storage paths, payment records, analytics, and support tools at once. A tenant is therefore a business boundary first and a database field second.
Ask who can sign a contract, configure a storefront, appoint administrators, receive or reconcile funds, and request all associated data. If the same entity answers those questions, it is probably one tenant. Its creators, moderators, customers, and finance staff are users inside that tenant. Separate tenants are warranted when two entities must not see or change one another’s commercial information, even if they share the same platform owner and streaming network.
Do not confuse a tenant with a deployment. Many tenants can occupy one deployment, while a regulated or unusually large tenant can later move to dedicated resources without changing its business identity. Keeping that mapping explicit makes regional hosting, premium isolation, and live streaming platform migration operational choices instead of account-model surgery. The immediate action is to write a one-sentence tenant definition before approving the data model.
What must be isolated and what can be shared?
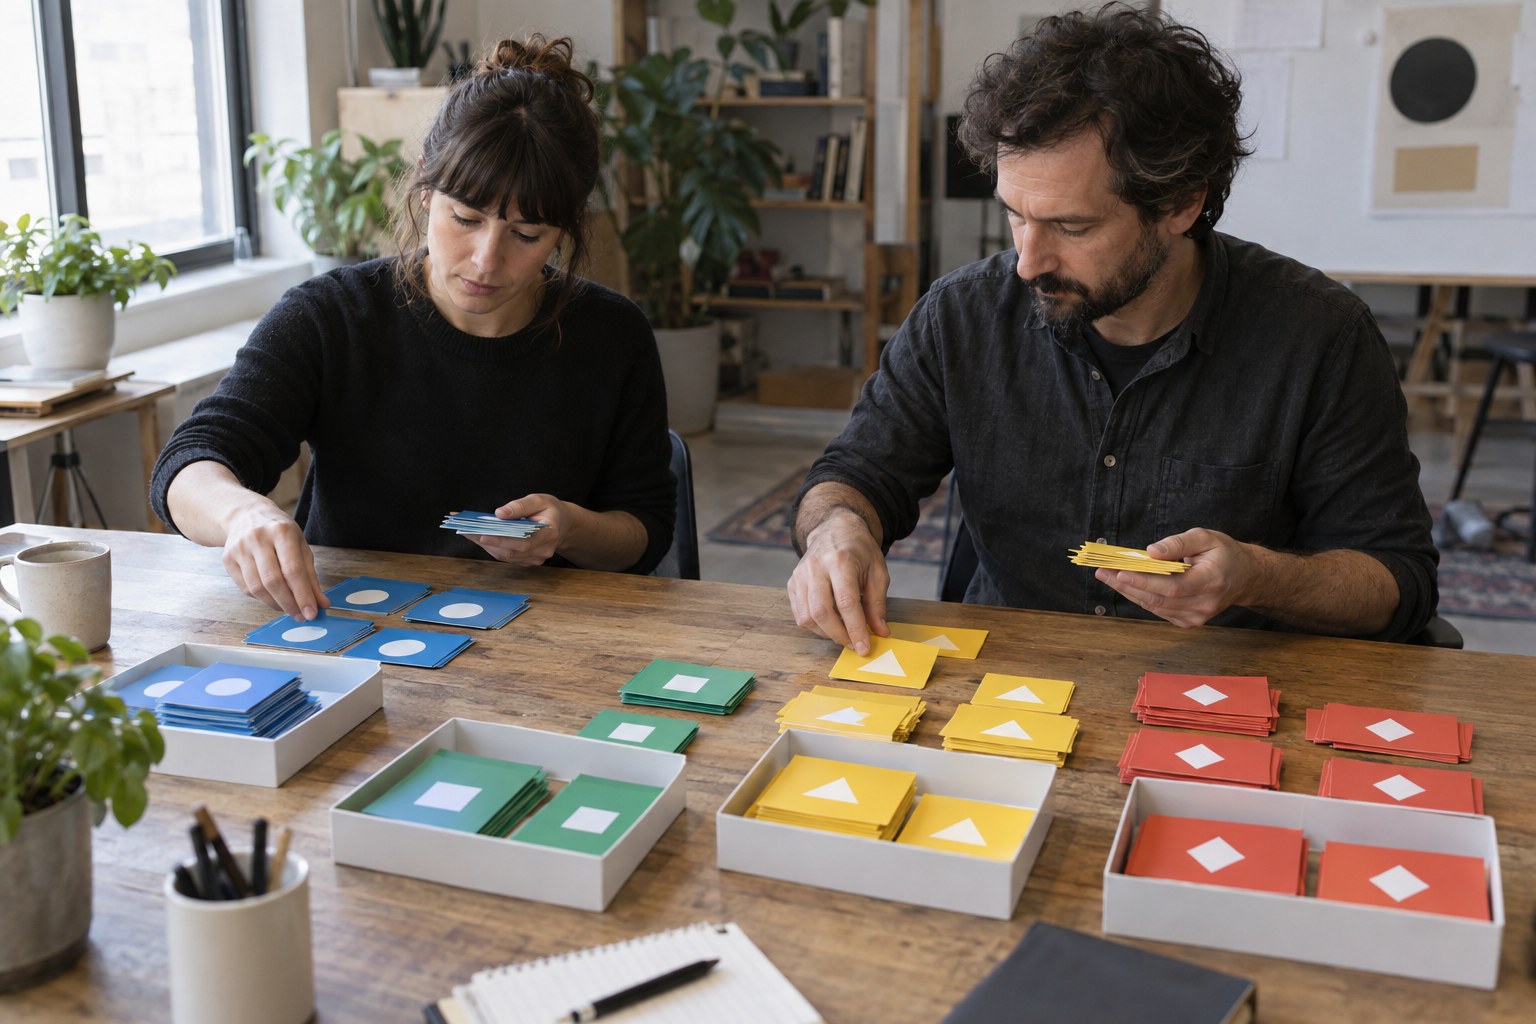
Isolate anything that defines identity, authority, money, policy, or business records. Share commodity delivery components only when every request remains tenant-scoped and one tenant’s demand cannot silently reduce another tenant’s service.
| Capability | Default boundary | Required control |
|---|---|---|
| Branding and domains | Isolate by tenant | Verified domain ownership, tenant-specific theme and routing |
| Users and permissions | Isolate membership and roles | Tenant ID on membership; deny cross-tenant role inheritance |
| Rooms and recordings | Isolate metadata and access | Tenant-scoped room, storage path, entitlement, and deletion |
| Payments and payouts | Isolate configuration and ledger views | Separate merchant settings, currencies, refunds, and reconciliation |
| Analytics and exports | Isolate raw and reported data | Tenant-filtered events, reports, export jobs, and audit trail |
| Moderation | Isolate queues and policy settings | Scoped cases, evidence access, escalation, and retention |
| Video transport | Share conditionally | Per-tenant quotas, observability, routing, and capacity controls |
Apply the matrix at every layer, not only in the customer-facing application. A correctly filtered dashboard is irrelevant if a background export, support console, cache key, webhook retry, or recording path omits the tenant identifier. For each capability, name its owner, tenant key, authorization check, storage location, retention rule, export route, and failure behavior. Unknown is not a boundary strategy; it is merely a breach report waiting for a date.
Private rooms also need viewer entitlements, expiring access, and recording rules that follow the same tenant boundary. Those controls belong in the wider secure live streaming design, but the tenancy decision comes first: security cannot reliably protect an asset whose business owner is ambiguous. Approve shared infrastructure only after its data and operational controls can be named.
How should shared streaming infrastructure resist noisy neighbors?
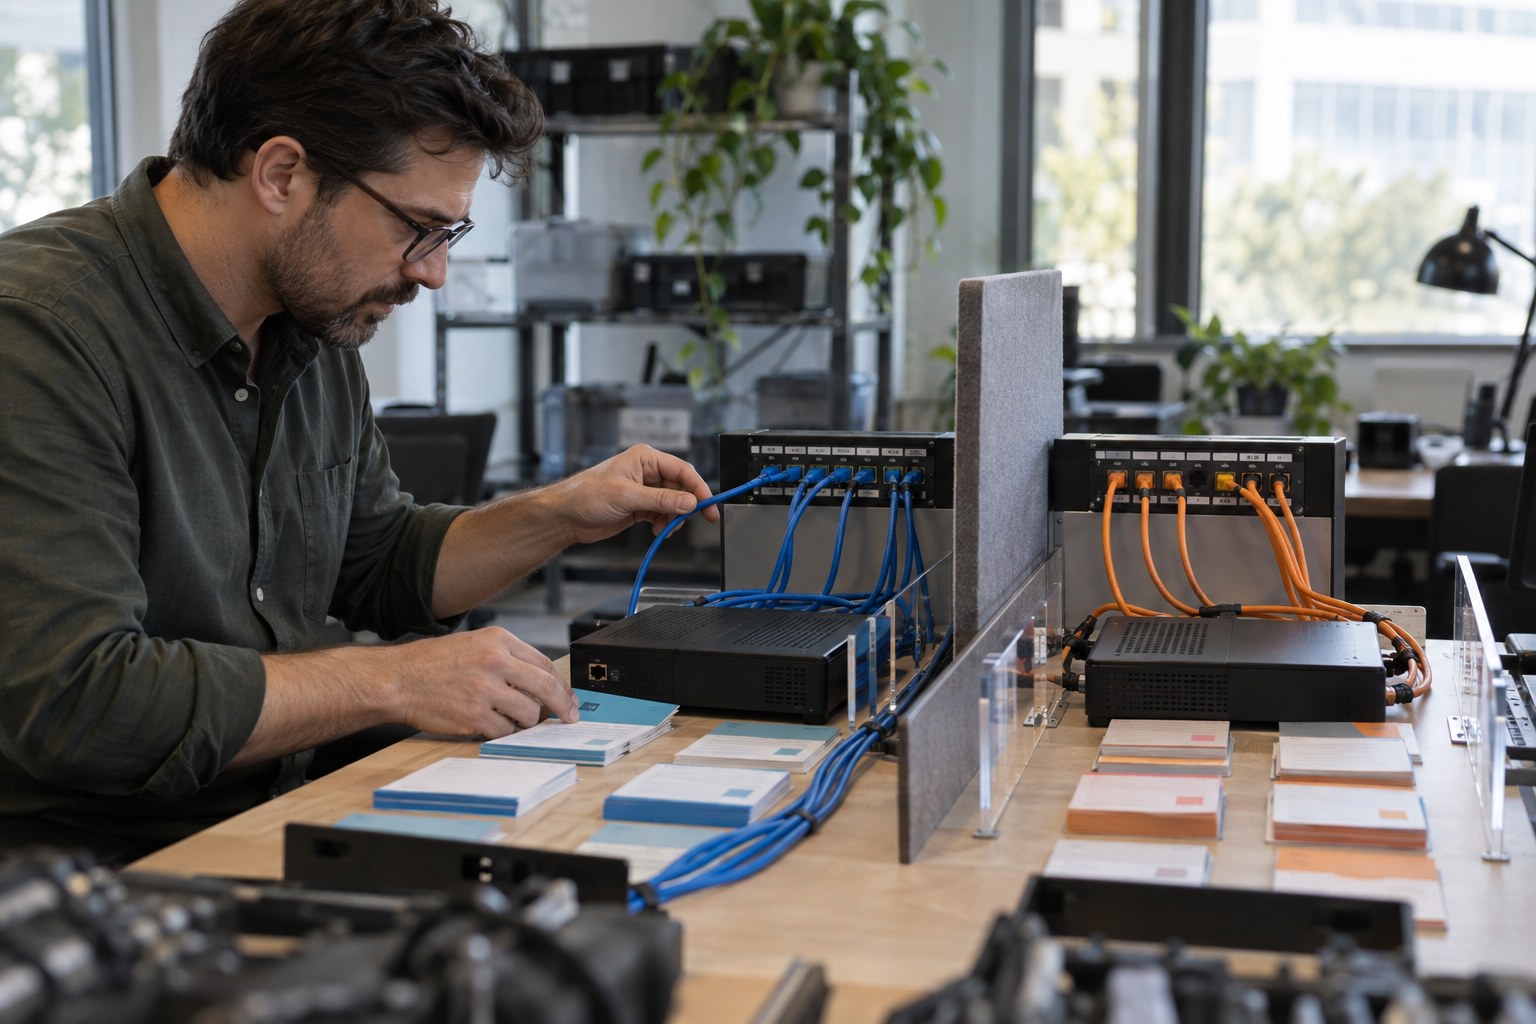
Shared media services need tenant-aware admission control, quotas, measurements, and routing. Average platform capacity is not enough: the system must show what happens to other tenants when one tenant creates a sudden broadcast, chat, recording, or export load.
WebRTC suits interactive private sessions and small groups where conversation latency matters; RTMP commonly serves contribution workflows and can feed broader distribution paths. A platform may support both, but the tenant boundary must survive protocol changes. Room authorization, tokens, recording ownership, chat, billing events, and moderation evidence should resolve to the same tenant before media admission. Review the underlying video streaming infrastructure separately from commercial configuration so scaling work cannot bypass access rules.
- Create two representative tenants with distinct domains, staff, rooms, payment settings, moderation queues, and analytics views.
- Apply a heavy but approved broadcast, chat, recording, and export workload to the first tenant while the second runs its normal workload.
- Verify admission limits, queue separation, media quality signals, error rates, and processing delays by tenant rather than only platform-wide.
- Force a failed worker, exhausted quota, delayed webhook, and interrupted export; confirm that retries preserve the tenant key.
- Inspect support tools, logs, recordings, reports, and downloadable files for cross-tenant identifiers or unauthorized access.
- Repeat after moving one tenant to another deployment and confirm that routing changes without changing identity or permissions.
Define pass criteria before running the test: prohibited cross-tenant access must remain denied, tenant-scoped work must stay attributable, and overload must trigger a deliberate limit or reroute rather than unexplained degradation elsewhere. The next action is to make this test part of release acceptance, not an heroic exercise performed after a major customer arrives.
What does the tenant model look like in operation?
A sound model keeps commercial records separate while allocating shared capacity explicitly. The following example uses planning assumptions, not a performance promise, to show how a launch team can expose boundary failures before customers do.
Assume an operator launches three tenants: a coaching brand expecting 60 concurrent sessions at peak, an entertainment agency expecting 70, and a workshop business expecting 20. The planned combined peak is 150 concurrent sessions because 60 + 70 + 20 = 150. That figure is only a test input; real capacity depends on session type, participant count, video profile, recording, network path, and the chosen media architecture.
Give every tenant its own verified domain, administrator membership, room namespace, merchant configuration, ledger view, moderation queue, analytics partition, and export destination. Place all three on a shared deployment initially, but set tenant-level admission policies and preserve a tenant-to-deployment mapping. Run the agency at its assumed peak while exercising refunds, moderation cases, and exports for the other two. Then move the agency to another deployment and repeat authorization and reconciliation checks.
The outcome is a business decision, not merely a load-test graph. If the agency’s workload remains attributable and the other tenants retain correct access, reporting, and processing, sharing is defensible. If isolation fails, separate the affected service or deployment before launch. A live streaming platform with tipping and private shows needs this commercial test because smooth video cannot compensate for a tip, private-room entitlement, or refund appearing under the wrong tenant.
How do you implement the platform without overbuilding?
Start with business boundaries, enforce them in identity and data access, then add shared media capacity and operational controls. Dedicated infrastructure should remain an available exception, not the default architecture or an improvised rescue.
- Define the tenant owner, legal relationship, users, administrators, creators, viewers, and permitted cross-tenant roles.
- Inventory branding, domains, rooms, recordings, payments, ledgers, analytics, moderation, support access, retention, and exports.
- Require tenant context in authentication, authorization, database access, cache keys, jobs, storage paths, webhooks, logs, and audit events.
- Choose WebRTC, RTMP, recording, and delivery paths by interaction model; attach tenant-aware admission and quota controls.
- Build provisioning, suspension, deletion, export, deployment assignment, and tenant-migration operations that administrators can audit.
- Run authorization, noisy-neighbor, payment-reconciliation, moderation, backup, restore, and migration tests before onboarding live businesses.
A custom build can make sense when the operating model is genuinely unusual, but building commodity streaming, chat, payments, and administration from zero delays validation. A white-label foundation is stronger when it already matches the revenue model and can be customized around the tenant rules that distinguish the business. Compare the boundary matrix, payment ownership, deployment options, and support workflow—not the length of a feature checklist. Founders still deciding how to create a live streaming website should settle ownership and tenancy before visual polish.
The verifiable next action is a design review using two fictional tenants. Attempt cross-tenant administration, room entry, reporting, refunds, moderation access, recording retrieval, and export. Record every control that blocks the attempt and every shared component affected by load. Any path that depends on staff remembering the correct tenant is unfinished. This review also exposes when a private live streaming platform needs dedicated resources rather than logical isolation alone.
Turn the tenant model into a launchable platform
Once the boundary matrix is explicit, the buying decision becomes clearer: you need a platform whose branding, real-time video, monetization, administration, and payment integration can support the business model without surrendering ownership. Scrile Stream provides a white-label foundation for branded webcam and video-chat services, including private and group video, pay-per-minute access, tips, premium content, built-in chat, direct payment integrations, and administration tools.
Scrile also offers custom development, UX/UI support, hosting, technical support, and project management for teams whose tenant rules require more than configuration. Evaluate the foundation against your two-tenant test, then scope the required isolation, monetization, and deployment work before committing to a roadmap.
Frequently asked questions
What is a multi tenant live streaming platform?
It is one streaming product that serves multiple independent businesses or brands while separating their identity, configuration, users, permissions, commercial records, moderation work, analytics, and exports.
Is a creator the same as a tenant?
Usually not. A creator is commonly a user within an agency, marketplace, school, or platform tenant. A creator should become a tenant when they independently control branding, administrators, commercial settings, and data rights.
Can tenants safely share WebRTC or RTMP infrastructure?
Yes, if admission, tokens, room ownership, recording, measurements, quotas, and failure handling remain tenant-scoped. The protocols themselves do not create the business boundary.
Which data should never leak between tenants?
Credentials, roles, room access, recordings, payment settings, ledger entries, customer activity, moderation evidence, analytics, exports, and private configuration must remain within their authorized tenant boundary.
Does every tenant need a separate database?
No. Logical isolation can be appropriate when tenant identifiers, authorization, queries, jobs, caches, storage, audits, and tests enforce the boundary. Dedicated databases may be warranted by risk, scale, region, or contract.
How do you test for noisy-neighbor problems?
Load one tenant’s broadcasts, chat, recordings, and exports while another runs normally. Inspect tenant-level admission, errors, processing, media signals, queues, retries, and access controls against predefined pass criteria.
When should a tenant receive dedicated infrastructure?
Consider it when contractual isolation, regulatory obligations, regional placement, unusual workloads, premium service requirements, or repeated contention cannot be addressed reliably with shared resources.
Can a white-label platform support a multitenant business?
It can when its identity, branding, payments, permissions, moderation, analytics, exports, and deployment model match the required tenant boundaries and customization is available for business-specific rules.